EXECUTIVE PERSPECTIVE
The defining question for agent-supported supply chain planning is not whether software can produce a recommendation. It is whether an enterprise can identify precisely where analysis ends and authority begins. A planning agent may investigate exceptions, collect evidence, compare alternatives, and draft actions. Those capabilities can be useful without authorizing the system to release purchase orders, reallocate scarce inventory, change production schedules, or revise customer commitments.
Advanced planning and scheduling (APS) tools remain important because they model feasibility and constraints. An agent-oriented layer may help coordinate work across planning, procurement, operations, logistics, and finance. Yet the quality of that coordination depends on the reliability of source records and the organization's approval design. The NIST AI Risk Management Framework identifies governance, mapping, measurement, and management as complementary functions for responsible AI use.¹ That is an appropriate starting point for a controlled planning workflow.
THE DECISION GAP BETWEEN ANALYSIS AND ACTION
Consider a hypothetical disruption: a supplier reports that a component will arrive four days later than expected. APS may show which production orders could be resequenced. Inventory systems may show stock at another site. A logistics provider may offer expedited movement. Commercial teams may hold commitments that are not visible to a scheduling model.
The agent's first useful contribution is to assemble the decision context: what happened, which records are authoritative, which facts remain disputed, which options are feasible, and which person owns the choice. Its role should be explicit. A system that compiles a recommendation is not equivalent to a system authorized to execute it.
This distinction matters most when an apparently reversible change has consequences elsewhere. Moving inventory could protect one customer while creating a shortage for another. Expediting could improve service while increasing cost. Substituting a product may require quality or regulatory authorization, especially in healthcare. A plausible recommendation is therefore insufficient; the organization needs a defensible decision record.
A FOUR-LEVEL AUTHORITY MODEL
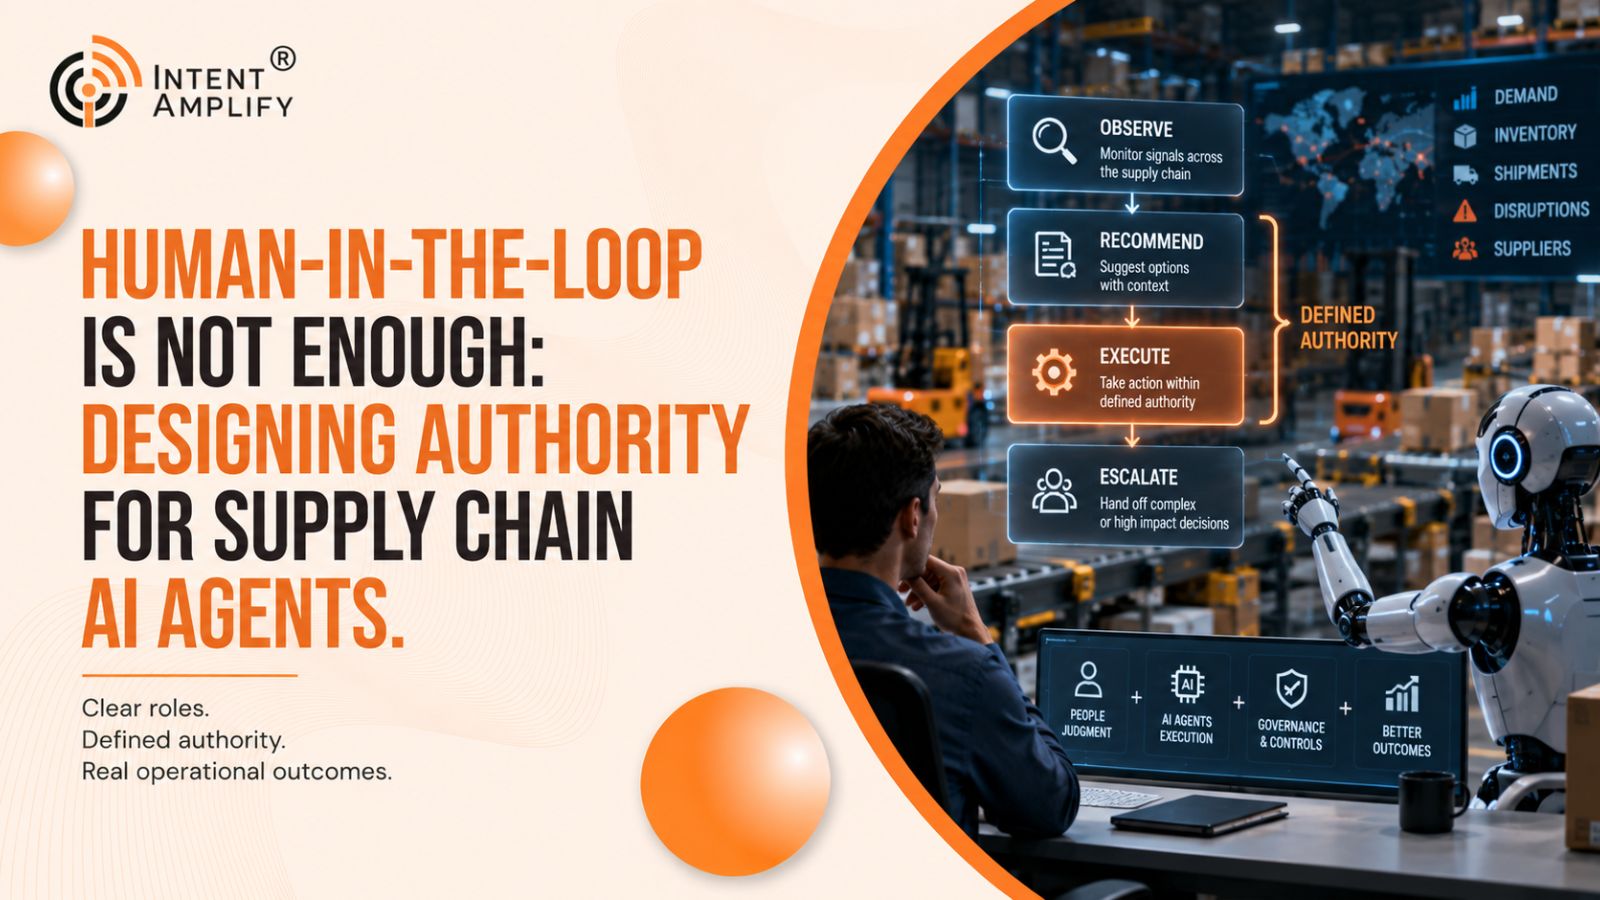
- Level one — observe. The system reads approved sources, detects a defined exception, and prepares a concise summary. It cannot modify operational records. This is the safest place to test evidence quality.
- Level two — recommend. The system compares scenarios, documents assumptions, and identifies an appropriate approver. It can explain why one option appears preferable but must surface uncertainty and choices.
- Level three — prepare for execution. After a human approves the recommendation, the system may assemble a proposed purchase-order change, transfer request, or revised schedule for final verification. Approval and execution remain distinct controls.
- Level four — bounded execution. The system may take specifically authorized actions within defined monetary, product, geographic, and operational limits. This level requires tested safeguards, rollback where feasible, exception escalation, and detailed audit trails.
These levels are an editorial governance model, not a claim that any named platform implements them. ISO/IEC 42001 specifies requirements for organizational AI management systems and continuous improvement; it offers a useful management-system perspective when deciding how authority should be assigned and reviewed.²
THE APPROVAL PACKET LEADERS SHOULD REQUIRE
Every material recommendation should carry an evidence packet. It begins with the triggering event and its timestamp. It identifies the systems consulted, data freshness, the relevant inventory or capacity definitions, and any contradictions between sources. It lists the available options using a common comparison horizon.
The packet should distinguish mandatory constraints from preferences. Product eligibility, quality holds, customer contracts, and safety requirements may be non-negotiable. Cost, service level, and inventory balancing may involve trade-offs. The recommendation should explain the basis of its ranking and what would change the result.
Finally, it should name the decision owner, approval deadline, proposed action, and escalation path. The OECD AI Principles emphasize transparency, human oversight, accountability, and traceability across the AI lifecycle.³ Those principles become operational when the reviewer can inspect not just the recommendation but the inputs and reasoning path that informed it.
WHEN HUMAN REVIEW MUST BE NON-NEGOTIABLE
Human approval should remain mandatory where the action affects regulated product eligibility, a customer-facing commitment, a material financial exposure, an exception to contractual terms, or an irreversible operational change. Thresholds must be set by the enterprise rather than inferred from generic technology marketing.
For healthcare-related inventory, a stock transfer may require verified item identity, lot or batch details, expiration data, and the status of applicable quality controls. GS1's Global Traceability Standard provides a framework for interoperable identification and traceability across supply chains.⁴ Traceability records are decision inputs, not an automatic grant of permission.
An effective workflow must also know when to stop. Missing source data, contradictory availability numbers, an unauthorized substitution, or a recommendation outside policy should trigger escalation rather than silent completion. A controlled refusal to act can be evidence of sound system design.
MEASURING WHETHER OVERSIGHT IS WORKING
The first evaluation should focus on decision quality. Measure whether evidence packets contain required fields, whether approvers can reproduce the recommendation's assumptions, whether conflicts are disclosed, and whether the correct owner is contacted. Record the rate of human corrections and the reasons for overrides.
Only then evaluate speed and business outcomes: time from exception to approved decision, schedule stability, avoidable expediting, inventory exposure, and service results. Use a baseline, comparable cases, and documented attribution limits. A faster recommendation does not automatically establish a better decision or a financial return.
NIST's Generative AI Profile describes additional considerations for evaluating and managing generative AI risks.⁵ Its cross-sector guidance reinforces the need for testing, monitoring, and clear accountability rather than assuming that model fluency proves operational reliability.
IMPLEMENTATION SCENARIO
A director selects a recurring supplier-delay exception. The pilot receives read-only access to a controlled set of planning, inventory, and supplier records. For ten historical cases, the team reconstructs what information was available before the original decision and asks the agent to prepare alternative responses.
Procurement checks supplier assumptions; planning checks feasibility; finance reviews cost exposure; quality checks any product restrictions; and the designated owner decides whether the recommendation would have been actionable. The team logs missing evidence, incorrect inferences, and ambiguous approvals. No customer benefit is asserted until independently measured.
After the read-only stage, the organization may test a proposed-action workflow. Permission to execute should be a separate governance decision, not the automatic next step after a promising demonstration.
Approval-Boundary Workshop: Make Autonomy Conditional
An enterprise can clarify the human approval boundary by building an action register before selecting technology. For each recurring exception, name the action the system may propose, the evidence it must show, the system it would change, and the person authorized to approve it. Distinguish read-only investigation, recommendation drafting, approval routing, and actual transaction execution. These are different permission levels and should not be described collectively as autonomy.
Test the register against three failure modes.
- First, a recommendation is plausible but based on inventory data that is out of date.
- Second, the suggested substitution is operationally feasible but lacks a required quality or customer approval.
- Third, an apparently minor reschedule creates a material downstream service impact.
In each case, define the stop condition, escalation path, and audit evidence before allowing any automated action.
A practical control matrix can record action category, affected system, permitted role, monetary or service-impact threshold, required checks, exception handling, and rollback procedure. For sensitive changes, use dual review or a second-system confirmation where organizational policy requires it. The agent should not infer authority from the fact that a user requested an action.
Pilot evaluation should include approved versus rejected recommendations, reasons for rejection, attempts to act beyond scope, completeness of evidence, and time to resolution. Review exceptions by severity, not only aggregate averages. The goal is to learn which bounded tasks can be supported reliably while preserving accountable human decisions for actions with material consequences.
A Practical Escalation Rule
A proposed planning action should pause when the source timestamp is missing, the required quality or customer approval is absent, or the execution impact exceeds the named approver's authority. The pause should produce a reason code, the missing evidence, and a responsible owner - not an opaque failure message. Teams can test these rules against past exceptions and document how often a human had to supply information that the workflow could not retrieve.
CONCLUSION
The practical breakthrough beyond APS may lie in the quality of the decision workflow rather than the removal of the decision-maker. Start with the exception, preserve evidence, define approval rights, and earn any expansion of autonomy through measured results.
READ THE RELATED WHITEPAPER
Beyond APS: Why Your Next Supply Chain Breakthrough Is a Planning Agent
REFERENCES
1. National Institute of Standards and Technology, AI RMF Core
https://airc.nist.gov/airmf-resources/airmf/5-sec-core/
2. International Organization for Standardization, ISO/IEC 42001:2023 — AI Management Systems
https://www.iso.org/standard/42001
3. OECD, AI Principles
https://www.oecd.org/en/topics/ai-principles.html
4. GS1, Global Traceability Standard
https://www.gs1.org/standards/gs1-global-traceability-standard/current-standard
5. National Institute of Standards and Technology, Generative AI Profile